Key Takeaways
- KREMLIN Malware installs fake Chrome and Edge extensions to steal banking data
- The operation targets Brazilian bank customers using blockchain-hidden servers
- Researchers found over 1,500 infected systems, mostly in Brazil
Security researchers have identified a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. The malware secretly installs harmful browser extensions to steal login details and banking data from victims.
How the Attack Works
Elastic Security Labs tracks the group behind the campaign as REF9334. The threat actor has been active since at least May 2025 and uses fake messages that pretend to be from a dozen Brazilian banks to trick people into opening harmful files.
The attack begins with a JavaScript file disguised as a banking document, invoice, or company file. Once a victim opens it, the file triggers a multi-stage process that installs additional harmful programs in steps, checking first that it is not running inside a security testing environment.
The KREMLIN Malware then sets up long-term access on the infected computer and contacts an Ethereum blockchain smart contract to receive updated server addresses. Using blockchain this way makes it harder for investigators to shut down the attacker’s infrastructure since the addresses can change without warning.
Extension Steals Data From Browsers
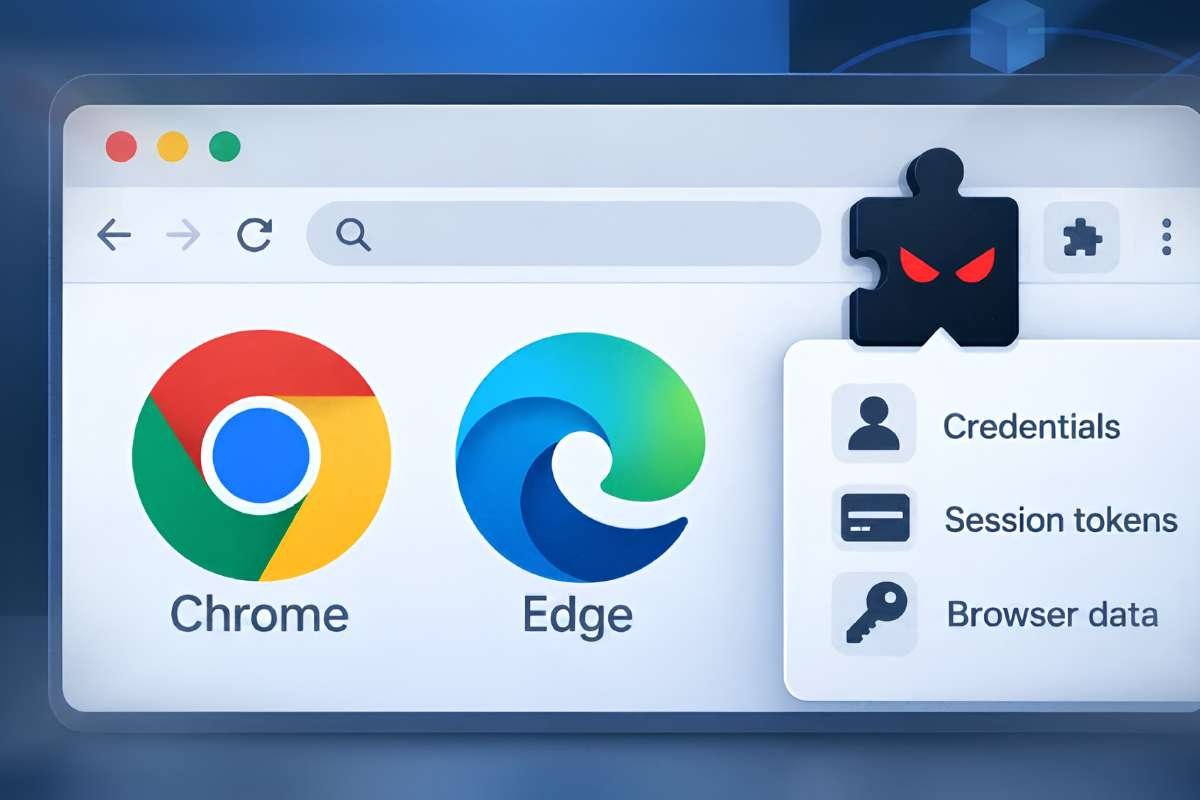
Once installed, the malicious browser extension associated with the KREMLIN Malware requests broad access to browser tabs, cookies, and stored data, then sends stolen information to a remote server. It also creates a unique ID for each victim, which is included in every message sent back to the attacker.
The extension can take screenshots of open tabs, list visited websites, steal saved cookies and site data, collect browsing history, and copy full webpage content. It communicates with attacker servers by disguising its network requests as ordinary website stylesheet files, helping it avoid detection by security tools.
Researchers say the extension uses a known method called “Phantom Extension” to bypass Chrome’s built-in security checks without triggering warning systems, allowing it to install without the user’s knowledge.
Thousands of Systems Affected
Elastic registered one of the KREMLIN Malware’s monitoring domains and found more than 1,500 infected devices attempting to connect to it, with over 98% located in Brazil. This discovery temporarily disrupted part of the malware’s built-in defenses, giving security teams extra time to detect and clean infected devices.
Investigators believe the group has run seven separate campaigns since June 2025 and previously relied on other well-known malicious programs before shifting to blockchain-based infrastructure in May 2026.
What Users Can Do
Security experts recommend that computer users avoid opening unexpected file attachments, especially ones claiming to be invoices or bank documents. Reviewing installed browser extensions regularly and removing unfamiliar ones can also reduce risk.
Keeping browsers and antivirus software updated helps block known attack methods. Users who bank online should watch for unusual account activity and enable extra login verification steps where available.
This discovery adds to a growing pattern of attackers using KREMLIN Malware and browser extensions as a way to bypass standard security protections. Security researchers continue monitoring the group’s activity to protect users from further attacks.
Visit CyberPro Magazine For The Most Recent Information.